BluePrint Protect™ · Third-Party Risk Management
BluePrint Protect™ brings security into the buying process, so your team can assess vendors and their products before the contract is signed and track findings through remediation. Know the risk before it becomes yours.
The 2024 Change Healthcare attack demonstrated the impact a third-party disruption can have on hospitals and patient care.
Source: American Hospital Association, March 15, 2024; survey of approximately 1,000 hospitals.
Stay in control as vendor volume grows.
Bring assessments, evidence, findings, and follow-up into one workflow.
Send customized questionnaires and collect vendor documentation before the contract is signed. Use the evidence to approve with confidence, set stronger terms, or choose another path.
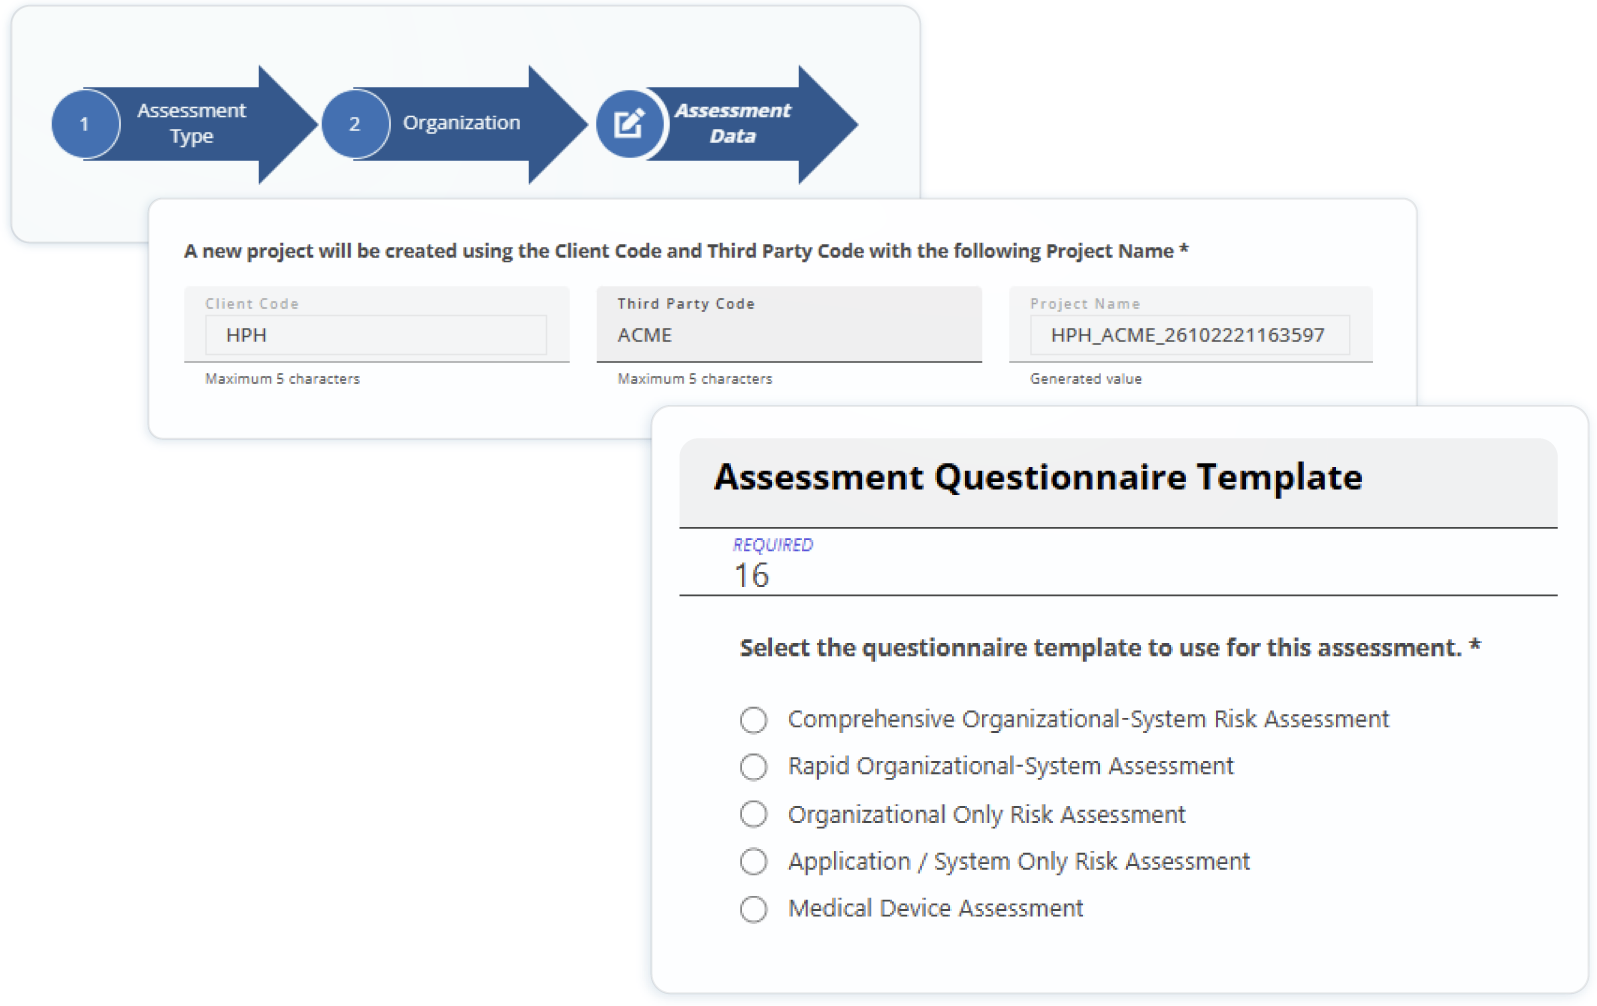
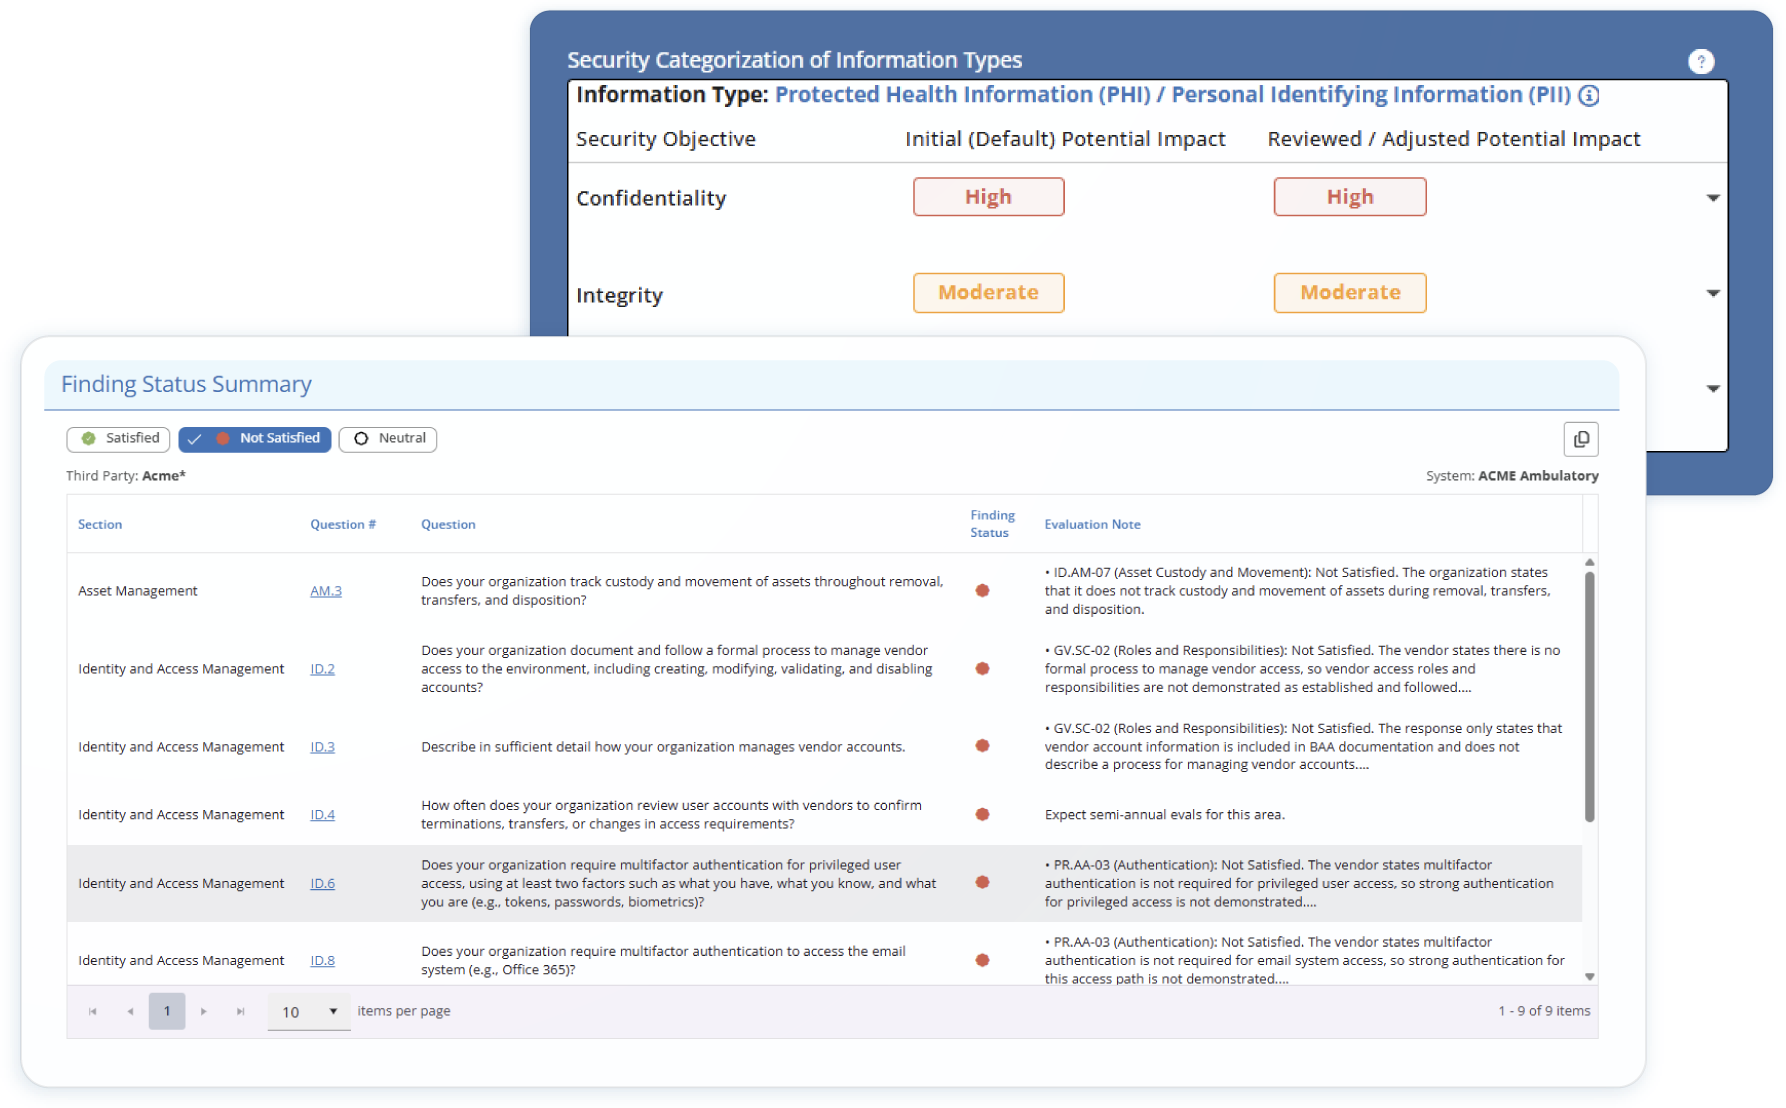
Fit-for-purpose assessments cover both the vendor organization and the product or system, so you see risk in the applications your team relies on.
Automated follow-up and AI-assisted review carry findings through remediation, exceptions, and reassessment. Stakeholders and vendors work from one place, and your team keeps final judgment.
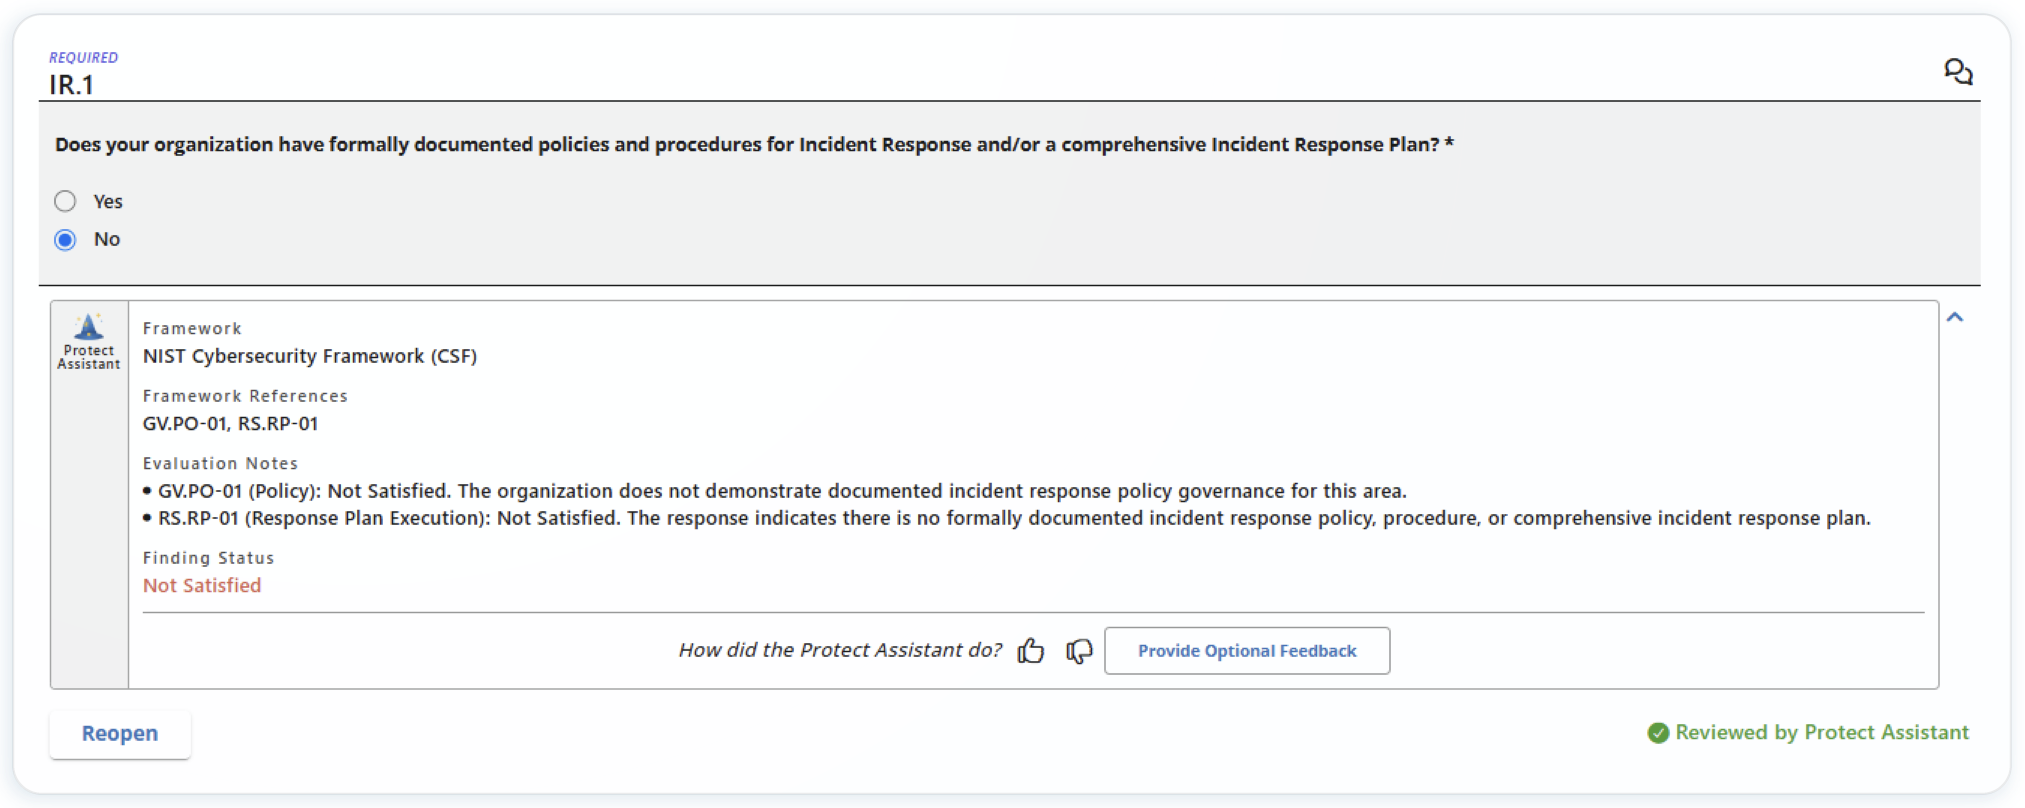
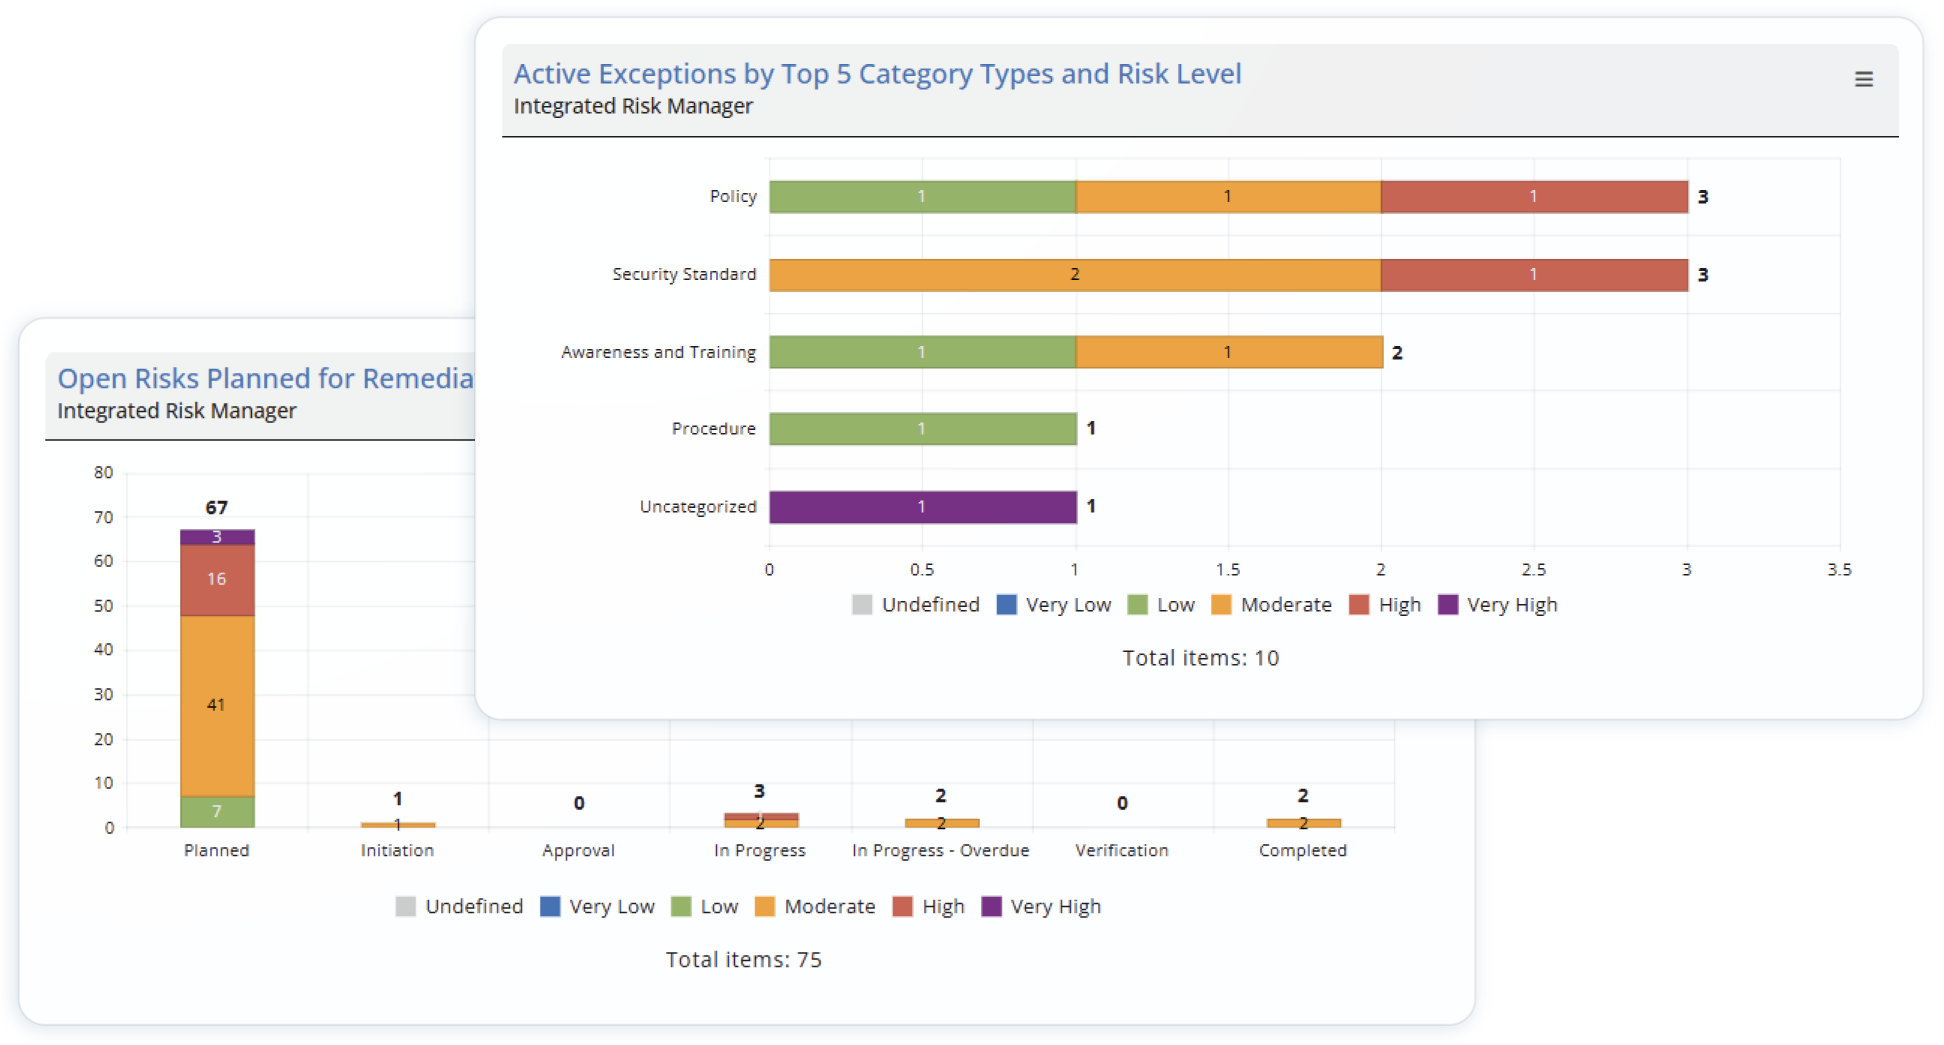
One record connects each vendor to its systems, assessment history, risk status, and owner. NIST-based scoring and dashboards show where risk stands and what needs action.
Assess vendors before you sign, then carry findings through remediation and reassessment.
01
Organize vendors and set assessment priority based on risk.
02
Request questionnaires and supporting security or compliance documentation.
03
Evaluate exposure, score risk against NIST, and document what needs attention.
04
Assign owners, track progress through remediation and exceptions, and reassess as needed.
Trusted by Healthcare Security and Risk Leaders
Miroslav Belote
Chief Information Security Officer
Valley Health System
Explore how healthcare teams have used Intraprise Health solutions to support cybersecurity risk management.
Frederick Health combined BluePrint Protect IRM, the NIST Cybersecurity Framework, and leadership education to support a shared language for discussions of risk and priorities.
Read the case study
Pomona Valley began with HIPAA One for compliance work, then expanded to third-party risk management, NIST assessments, and BluePrint Protect IRM.
Read the case study
Run the program yourself, share the work with Intraprise Health, or have Intraprise Health lead it. Adjust the model as vendor volume, capacity, and priorities change.
Learn how BluePrint Protect™ could support your organization’s vendor risk management process.


